
Containment is the backbone of effective incident response. It’s the step that stops threats from spreading while your team prepares for recovery. Without a clear plan, businesses risk delays, increased costs, and regulatory penalties.
Here’s what you need to know:
- Containment vs. Fixing: Containment isolates threats (e.g., disconnecting infected systems) to prevent further damage, while fixing focuses on resolving the root cause.
- Why It Matters: The average ransomware dwell time is 6 days. Every hour without containment gives attackers more time to cause harm.
- SME Challenges: Smaller businesses often lack resources, leading to improvised responses. Clear authority and pre-approved actions are critical.
- Financial Impact: A tested incident response plan can cut breach costs by up to 50%.
- Regulations: Starting May 2026, CIRCIA requires reporting incidents within 72 hours and ransom payments within 24 hours.
Key Steps for SMEs:
- Assign roles like Incident Commander, Technical Lead, and Legal/Compliance.
- Pre-approve containment actions to act swiftly during a breach.
- Use tools like Endpoint Detection and Response (EDR) for network isolation.
- Preserve evidence (e.g., logs, screenshots) before making changes.
- Conduct tabletop exercises to test your plan and improve readiness.
Containment isn’t just about stopping threats – it’s about protecting your business and meeting compliance requirements. This guide provides actionable steps to strengthen your incident response strategy.
Governance Framework for Incident Containment
Setting Up Executive Oversight
Containing an incident effectively starts with decisions made well before any crisis arises. The most crucial of these decisions is straightforward: who has the authority to act?
Frameworks like NIST CSF 2.0 emphasize the importance of governance by making it a core function, highlighting the need for board-level accountability in incident response. This means executives must establish clear escalation paths, pre-approve critical decisions, and document these processes ahead of time.
One essential step is setting up an out-of-band communication channel – such as a Signal group or a separate Slack workspace – that leadership can rely on if the primary corporate network is compromised. These channels act as a safety net, ensuring that leadership can still communicate and coordinate during a crisis when regular systems may be unreliable.
Once oversight is in place, the next priority is assigning well-defined roles.
Key Roles and Responsibilities
A frequent misstep in small and medium-sized enterprises (SMEs) is assuming that the CEO should lead the incident response. This isn’t ideal – at least not operationally. Effective containment relies on separating the person managing the response from the one making high-level business decisions.
"The Incident Commander is the single decision-maker during an incident. Not the CISO. Not the CEO. The person who has authority to make rapid decisions." – Phillip (Tre) Bucchi, Founder, Valtik Studios
The table below outlines the key roles that every SME should assign before an incident occurs:
| Role | Primary Responsibility | Who Typically Fills It |
|---|---|---|
| Executive Sponsor | Acts as the board liaison, approves risk decisions, and oversees materiality judgments | CEO or CFO |
| Incident Commander | Leads the response, manages timelines, and makes rapid decisions | Senior IT Manager or Director |
| Technical Lead | Handles containment, forensics, and system isolation | Senior Engineer or MSP Lead |
| Legal/Compliance | Manages regulatory notifications and ensures evidence preservation | In-house GC or Outside Counsel |
| Communications Lead | Coordinates internal and external messaging, including PR | Marketing Lead or HR |
| Scribe | Maintains a real-time, time-stamped log of decisions for legal and insurance purposes | Any designated team member |
In smaller organizations, it’s normal for one person to take on multiple roles. However, leaving any of these functions unassigned is a recipe for chaos. The Scribe role, in particular, is often underestimated. A detailed, time-stamped log of decisions is critical for insurance claims, regulatory compliance, and post-incident analysis.
Aligning Containment Plans with Business Goals
A containment plan that disregards business priorities can sometimes create more disruption than the incident itself. For example, shutting down a payment processor during peak sales hours could have a bigger financial impact than the breach.
To avoid such missteps, it’s essential to define business continuity tiers in advance. Categorize systems into three groups:
- Critical systems: Revenue-generating systems that must remain online.
- Important systems: Productivity tools that can handle short outages.
- Deferred systems: Internal tools that can wait for restoration.
When the Incident Commander understands these tiers, they can make faster, more informed decisions about containment, minimizing unnecessary disruptions.
"An incident response plan is effective only when authority, timing, and evidence requirements are explicit." – Nandor Katai, Valydex
Public SMEs face additional challenges. For instance, the SEC’s four-business-day disclosure rule kicks in as soon as an incident is deemed material, not when it’s detected. Having a documented process for making quick materiality determinations is key to avoiding regulatory penalties and ensuring timely communication with investors. Additionally, most cyber insurance policies require notification within 24–72 hours of first awareness to maintain coverage. This makes having a strong governance framework just as critical as a swift technical response.
sbb-itb-c53a83b
Core Principles of Effective Containment
Speed vs. Accuracy in Containment
When an incident strikes, waiting to fully understand the situation before acting can waste precious time. The first hour isn’t about pinpointing the root cause – it’s about damage control. As Nandor Katai from Valydex explains:
"The goal is not perfect analysis in the first hour; the goal is controlled containment, continuity, and decision quality under pressure."
To avoid delays, pre-approve containment actions so you can act swiftly to isolate compromised systems. Stick to the 15-minute rule: confirm the event, assign leadership, and implement pre-approved containment measures. Once the immediate threat is neutralized, you can dive into a deeper investigation.
This rapid response sets the stage for the containment techniques we’ll explore next.
Containment Techniques for SMEs
Even without a dedicated security operations center, small and medium-sized enterprises (SMEs) can still manage containment effectively using straightforward methods and widely available tools.
Network isolation is often the first step. If you suspect a device is compromised, disconnect it from Ethernet or disable its Wi-Fi connection immediately. However, don’t power it off – volatile memory (RAM) might hold critical forensic evidence needed for insurance claims or legal proceedings.
"Isolate, do not eradicate. A wiped server is a destroyed crime scene." – Lorikeet Security
Account containment requires careful sequencing. For compromised accounts, first revoke active sessions and OAuth tokens, then reset the password. This prevents the attacker from maintaining access. Afterward, audit the account for suspicious settings, such as email forwarding rules, that could redirect sensitive data.
Here’s a quick breakdown of containment techniques:
| Containment Technique | Practical SME Method | Key Precaution |
|---|---|---|
| Network Isolation | Disconnect Ethernet, disable Wi-Fi | Do not power off to preserve volatile memory |
| Account Revocation | Disable user in M365 or Google Workspace | Revoke active sessions and OAuth tokens first |
| Endpoint Isolation | Use EDR tools (e.g., SentinelOne, Defender) | Ensure your MSP retains management plane access |
| Evidence Preservation | Screenshot errors, export audit logs | Capture logs before they roll over or get erased |
Another often overlooked step is creating an evidence packet before making any changes. At a minimum, this should include system logs, timestamps, screenshots of active sessions, and error messages. This documentation can be critical for insurance claims or regulatory compliance.
Internal and External Communication During an Incident
Once containment begins, clear communication ensures everyone stays informed and aligned. It’s also a key part of maintaining business continuity, as discussed earlier in this guide.
Designate a single Communications Lead to oversee all messaging. This person ensures consistent updates and reduces the risk of legal or reputational damage. They should control what employees, customers, and regulators are told.
Internally, keep communication channels separate. The technical team needs a focused channel for execution details, while leadership requires structured updates summarizing the situation’s severity, scope, completed actions, business impact, and next steps. Mixing these streams can lead to confusion and unnecessary noise.
For external communication, pre-drafted holding statements are a lifesaver. A simple message like "We are investigating a security event and will provide updates as more information becomes available" buys time to confirm facts before making public statements. Employees should also be instructed not to discuss the incident publicly or take independent actions – both could compromise evidence and weaken your legal position.
Lastly, ensure you meet all reporting deadlines. Your legal lead should know when notification timelines begin, which is why it’s crucial to pre-classify incident types and their reporting obligations long before a crisis happens.
IR Critical Phases: Mastering Containment and Recovery
Building an SME Containment Playbook
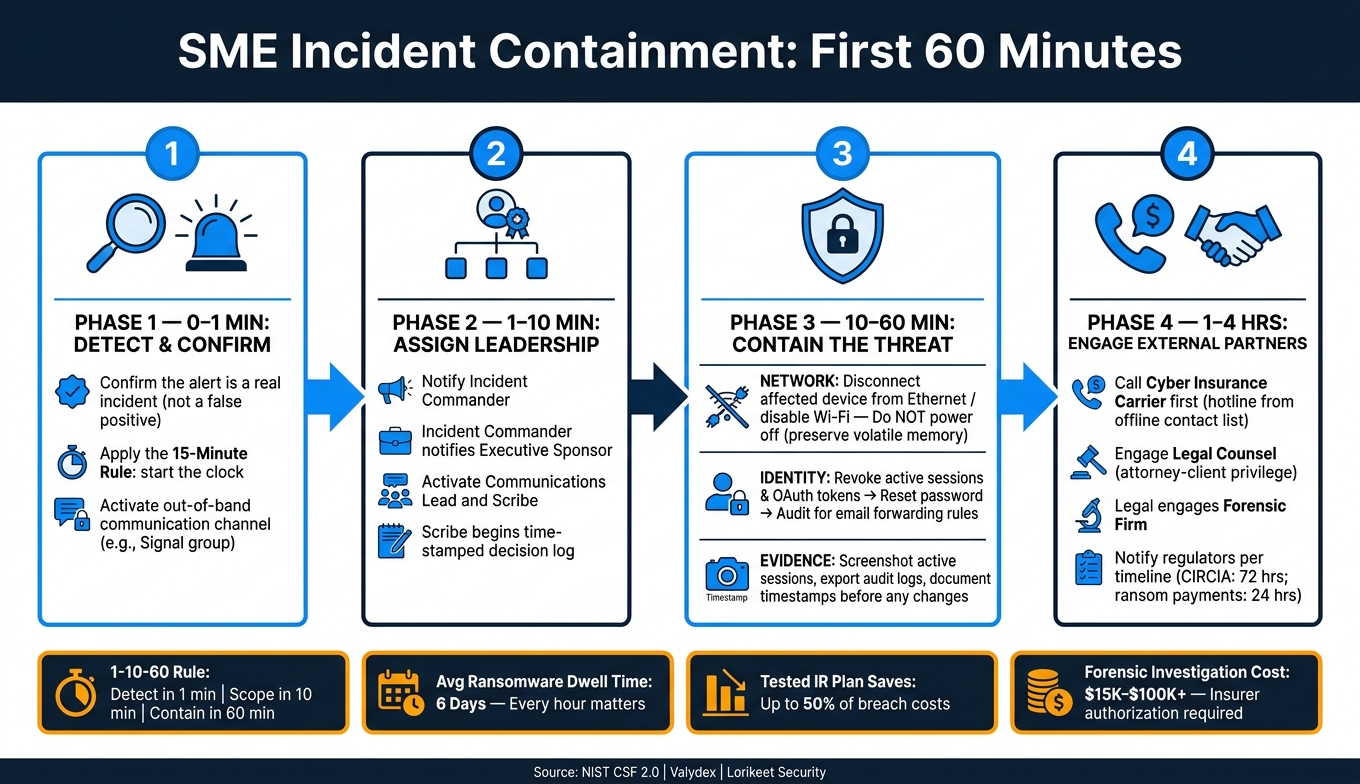
Incident Containment Response: First 60 Minutes for SMEs
Once governance structures and core containment principles are in place, the next step for SME executives is to create actionable playbooks that can guide their teams during crises.
Scenario-Based Planning
A playbook tailored to specific threats enables quicker decision-making compared to generic plans.
At a minimum, SMEs should prepare playbooks for key scenarios such as ransomware, business email compromise (BEC), data breaches, insider misuse, and cloud control-plane compromise. In 2026, two newer scenarios demand attention: AI data exposure (e.g., employees accidentally sharing sensitive information with unapproved AI tools) and AI deepfake BEC (where attackers use cloned voice or video to impersonate executives and authorize fraudulent transactions).
One common issue in scenario planning is a lack of clarity around decision-making authority. In 47% of executive tabletop exercises, the first 90 minutes are often wasted debating who has the authority to take critical systems offline. Your playbook should clearly define who can make decisions like shutting down the ERP system, disabling a cloud environment, or disconnecting a vendor connection – well in advance of a crisis.
"An incident response plan is effective only when authority, timing, and evidence requirements are explicit." – Nandor Katai, Valydex
Each scenario-specific playbook should outline immediate actions to be taken as soon as an incident is detected.
Immediate Containment Steps by Incident Type
For every incident type, your playbook should outline three key steps: isolate, reset identity, and close the persistence mechanism. The sequence of these actions is critical.
| Incident Type | Isolate | Reset Identity | Close Persistence |
|---|---|---|---|
| Ransomware | Disconnect affected segments from the network | Disable compromised privileged accounts | Identify and secure the initial access point |
| BEC | Lock the compromised mailbox and revoke all active sessions | Reset credentials and MFA methods | Remove new mailbox rules and external forwarding |
| AI Data Exposure | Identify the AI service and submitted data categories | Disable or restrict access to the unauthorized tool | Assess compliance risks for sensitive data |
| Insider Misuse | Silently restrict access and log all activity | Involve HR and Legal before confronting the individual | Preserve evidence before making account changes |
The insider misuse scenario requires extra caution. Confronting a suspected insider too soon can lead to evidence being destroyed or even retaliatory actions. It’s often safer to quietly restrict access and gather evidence before taking further steps.
Once these internal actions are underway, it’s essential to involve external partners promptly for additional support.
Working with External Partners During Containment
Your playbook should position external partners as essential collaborators, not just backup resources. One of the most critical steps within the first 1–4 hours is contacting your cyber insurance carrier, rather than your IT team or law enforcement. Insurance providers can quickly dispatch pre-approved forensic and legal teams. Acting without their authorization may jeopardize your coverage.
To maintain confidentiality, engage forensic firms through legal counsel, ensuring their findings are protected under attorney-client privilege. The sequence – insurer first, legal second, forensics third – often gets overlooked until it’s too late. Considering that third-party forensic investigations can range from $15,000 to over $100,000, early coordination with your insurer is crucial.
Assign a single internal vendor liaison to handle all communications with external partners during containment. Keep your emergency contact list – including the insurer’s hotline, your MSP’s after-hours number, and your legal counsel’s direct line – in a physical or offline format. This ensures access to critical contacts even if ransomware renders your email or internal systems inaccessible.
Continuous Improvement and Readiness
Long-term operational resilience isn’t achieved by chance – it’s built through ongoing refinement. Effective containment frameworks and scenario planning lay the groundwork, but continuous improvement ensures they stay relevant. This means regularly testing your containment plan, measuring its performance, and learning from every incident.
Metrics for Measuring Containment Effectiveness
Metrics provide a clear picture of your containment capabilities. For small and medium-sized enterprises (SMEs), the critical metrics include:
- Mean Time to Detect (MTTD): How quickly you identify a threat.
- Mean Time to Contain (MTTC): The time it takes to contain the incident.
- Mean Time to Recover (MTTR): How long it takes to resume normal operations.
High-performing organizations aim for an MTTD of 6–12 hours. A practical benchmark to strive for is the 1-10-60 rule: detect an alert within 1 minute, scope the issue in 10 minutes, and begin containment within 60 minutes.
On the qualitative side, metrics like Decision Quality and Evidence Integrity help assess the effectiveness of your response process. Another useful indicator is the Corrective-Action Closure Rate, which measures how effectively your organization addresses high-priority remediation tasks after an incident. This quarterly metric shows whether you’re learning from incidents or simply moving on.
"Resilience is not built during an incident. It is built in the deliberate, structured work that happens between incidents, when organizations choose to learn rather than simply move on." – Heights Consulting Group
These insights underscore the importance of regular, hands-on training exercises to maintain readiness.
Training and Tabletop Exercises
Having a tested incident response (IR) plan can make a huge difference. Organizations with such plans detect breaches 54 days faster and save an average of $2.66 million per incident compared to those without one. For SMEs, tabletop exercises (TTX) are a practical way to test your plan. These 2–4 hour sessions simulate realistic scenarios – like ransomware attacks or email compromises – without disrupting operations. Aim to conduct these exercises at least twice a year, or quarterly if there are significant changes in staff, vendors, or systems.
To make these exercises more impactful, use "inject cards" that introduce unexpected challenges. For example, “your backups are also encrypted” or “a reporter is calling for comment” can test your team’s ability to adapt under pressure. Be sure to include a range of stakeholders, from Legal and HR to executive leadership, to ensure a well-rounded response.
"An IR plan that has never been exercised is a plan that will fail when activated." – Lorikeet Security
After each exercise, hold a structured debrief to identify lessons learned and assign clear ownership to follow-up actions. This ensures that insights lead to tangible improvements.
While rigorous training is essential, many SMEs also benefit from external guidance to integrate these practices into daily operations.
Using Strategic Advisory Services
For SME leaders, the challenge often isn’t understanding the importance of continuous improvement – it’s finding the time to prioritize it. Containment planning can easily take a backseat to pressing concerns like hiring, revenue goals, and other operational demands.
This is where outside advisory services can help. Growth Shuttle, for example, works with CEOs of teams ranging from 15 to 40 people, helping them weave incident readiness into their day-to-day management processes. These services act as a strategic partner, helping executives refine their plans, close process gaps, and communicate technical security needs in a way that resonates with boards and investors.
Containment readiness isn’t just a technical task – it’s a critical operational discipline that deserves the same attention as any other core business process.
Conclusion: Key Takeaways for Executives
Incident containment is not a one-time task – it’s an ongoing process. Having a written incident response plan can make a huge difference, potentially reducing average breach costs for small-to-medium businesses (SMBs) by up to 50%. Organizations with formal plans can save around $2 million compared to those without one. Considering that the average data breach costs SMBs $149,000 and that 60% of small businesses shut down within six months of a successful cyberattack, the financial and operational stakes couldn’t be higher.
As Nandor Katai highlights, "an effective response demands clear authority, timely action, and preserved evidence to ensure controlled containment".
Executive Checklist for Containment Readiness
Here’s a quick checklist to evaluate your organization’s preparedness:
| Area | What to Verify |
|---|---|
| Governance | Designate an Incident Commander with documented authority and ensure an executive backup is in place. |
| Policy | Define severity levels (P1–P4) with clear escalation triggers and pre-approved containment actions. |
| Technology | Ensure 24/7-monitored EDR/MDR, immutable backups, and out-of-band communication channels are active. |
| Playbooks | Develop scenario-specific guides for ransomware, Business Email Compromise, and AI data exposure. |
| Training | Conduct and document a tabletop exercise within the last 12 months. |
| Accessibility | Keep an offline copy of the incident response plan and contact list, stored separately for emergencies. |
Accessibility matters. In 2025, a Fusion Computing client learned this the hard way. Their 14-page incident response plan named all roles correctly but was stored on SharePoint. When ransomware struck on a Saturday, the attacker took control of the Entra ID tenant, making the plan inaccessible. The team had to rely on a printed copy the CEO kept in his truck, which added three extra days of downtime. Without access, even the best plan is useless.
By addressing these critical areas, executives can ensure containment readiness and integrate it into broader business strategies.
Making Containment Part of Long-Term Business Strategy
Preparation doesn’t stop at immediate readiness. Executives must weave containment into their long-term strategies. This involves strengthening governance and conducting regular training exercises. Current trends in incident response prioritize governance as a central focus. Frameworks like NIST CSF 2.0 emphasize making containment a board-level concern rather than just an IT issue. In practice, this means tracking metrics like Mean Time to Detect (MTTD), Mean Time to Contain (MTTC), and Mean Time to Recover (MTTR) alongside traditional business metrics such as revenue and operational performance. This approach ensures that speed, clarity, and resilience remain core to the organization’s strategy.
New regulations are also pushing tighter timelines. Under CIRCIA (with the final rule expected by May 2026), businesses must report significant incidents to CISA within 72 hours and any ransom payments within 24 hours. Additionally, cyber insurers now often require documented evidence of annual tabletop exercises as part of their coverage conditions. Containment planning is no longer just good practice – it’s becoming a compliance and financial requirement. By embedding these practices into board-level discussions and compliance frameworks, SMBs can better position themselves for long-term resilience and operational sustainability.
FAQs
Who can authorize containment actions during a breach?
Clear lines of authority need to be set up ahead of time. The Incident Commander is usually the one to officially declare a security incident and give the green light for major actions, such as shutting down systems. Meanwhile, a technical lead can take immediate action on pre-approved measures (like isolating a host) as soon as threats are identified. For decisions that could lead to significant outages or costs, the final approval typically rests with an executive sponsor or their designated alternate. Growth Shuttle assists in outlining these roles to make decision-making more efficient.
What should we isolate first without destroying evidence?
When something goes wrong, the first step is to isolate the affected device from the network. Disconnect it from Wi-Fi or unplug the ethernet cable, but don’t power it down. Turning it off could wipe crucial forensic evidence stored in the device’s memory.
Containment should also extend beyond the device. This might mean isolating specific network segments, restricting access to certain devices or accounts, or revoking access tokens.
Throughout the process, keep a detailed, time-stamped log of every action you take. This helps preserve evidence and ensures there’s a clear record for accountability.
How do we meet CIRCIA’s 72-hour reporting deadline?
To comply with CIRCIA’s 72-hour reporting requirement, it’s crucial to set up clear internal processes that kick in as soon as a covered cyber incident is reasonably suspected. Keep in mind, the clock starts ticking after an initial credible assessment – not after completing a detailed forensic investigation. Submit a preliminary report with the facts you have, and provide additional updates as more information becomes available. Growth Shuttle can assist in organizing workflows, ensuring your team is ready to meet these obligations efficiently.