
If you only remember one thing, remember this: privacy by design is about how I build the system, while privacy by default is about how I set it up before anyone uses it.
For me, the article comes down to a simple split:
- Privacy by design = I put privacy into the product, system, and process from the start.
- Privacy by default = I turn on the most private settings from day one.
- Both are required under GDPR Article 25.
- GDPR fines can reach €20 million or 4% of global annual revenue, whichever is higher.
- For SMEs, this affects more than websites. It also touches CRMs, ERPs, analytics tools, billing systems, forms, admin panels, cookies, access controls, and retention rules.
Here’s the plain-English version:
- If I decide what data gets collected, who can see it, where it moves, and when it gets deleted, that’s privacy by design.
- If I decide which boxes are pre-checked, whether tracking starts right away, what fields are required, and who gets access by default, that’s privacy by default.
- One is mostly about system design. The other is mostly about settings and use.
- One needs proof like data flow maps, design docs, and access reports.
- The other needs proof like consent logs, config screenshots, and default-setting records.
Quick Comparison
| Criteria | Privacy by Design | Privacy by Default |
|---|---|---|
| Main focus | System build and data rules | Default settings and user-facing setup |
| When I apply it | Before and during development; after major changes | Before launch and in daily use |
| What it covers | Data flows, access logic, deletion, storage, sharing | Consent, tracking, forms, permissions, retention |
| Who usually owns it | Product, Engineering, IT, Legal | Marketing, CRM owners, RevOps, admins |
| Audit proof | Architecture diagrams, policy updates, logs | Consent records, field settings, config snapshots |
So if I’m running a small business, I shouldn’t treat this as two separate legal ideas. I should treat it as one workflow: build the system to limit risk, then launch it with tight settings already in place.
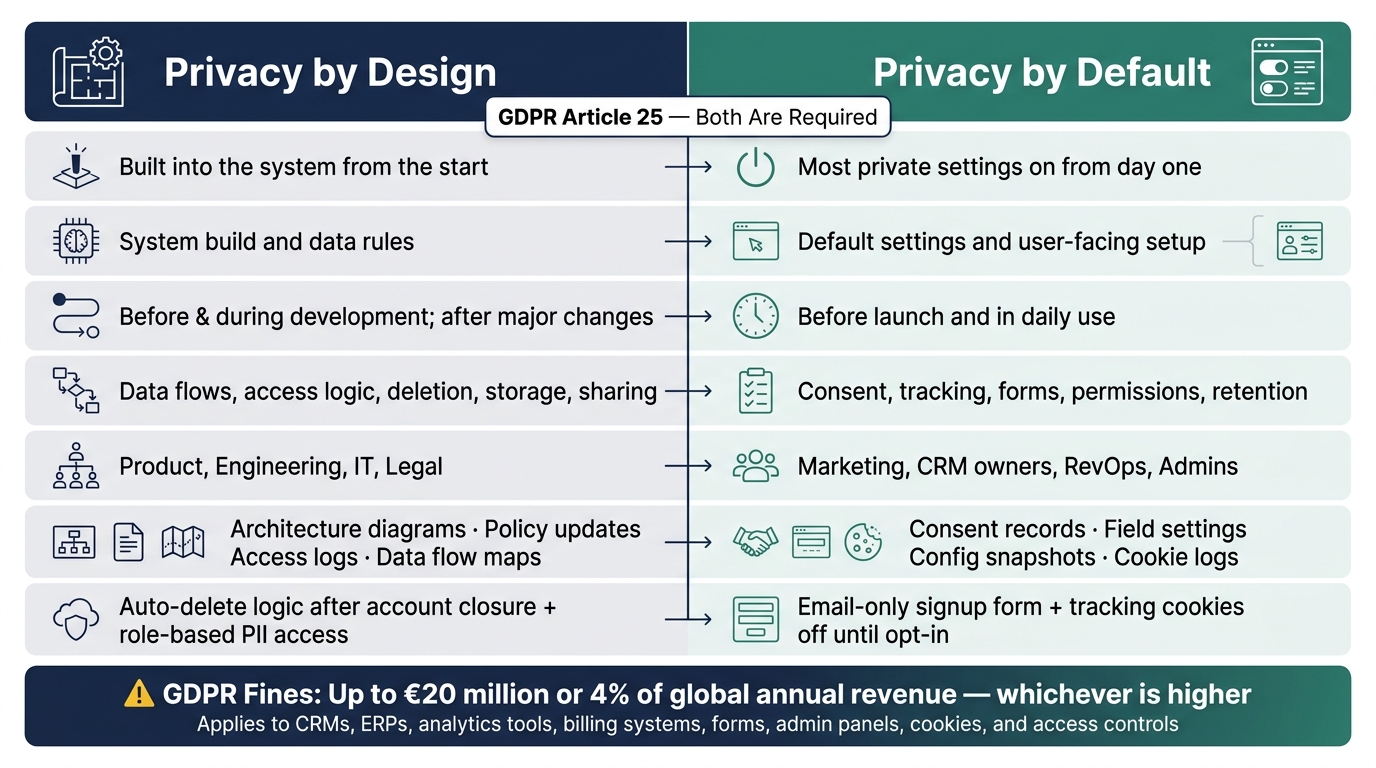
Privacy by Design vs Privacy by Default: Key Differences for SMEs
What is Privacy By Design And Default: Understanding the Concepts
sbb-itb-c53a83b
Privacy by Design: Built Into Products, Systems, and Processes
Privacy by design is not a pre-launch checklist. It’s an ongoing way of working that covers the full data lifecycle: what you collect, why you collect it, how you store and share it, and when you delete it.
For a product team, that means mapping data flows before engineering starts, then reviewing them again after any material system change. Put simply, privacy by design is a design-and-change discipline, not a launch task. It sets the architecture. Privacy by default sets the operating floor.
Many SMEs run several systems at once – CRMs, ERPs, and analytics platforms – and each one handles personal data in its own way. If those systems aren’t planned with care, the context around that data gets split across tools, and risk starts to pile up.
Scope, Timing, and Core Controls
Privacy by design works at the architecture level, not the settings level. The main controls focus on being clear about what data is collected, making sure it serves a specific purpose, and putting guardrails around who can access it and where it can move.
Because these controls shape the system itself, they need to be set before implementation starts. That includes role-based access, data handling rules, and credential control. For sensitive billing or PII systems, two-factor authentication adds another layer of protection.
Timing matters just as much as scope. Privacy reviews belong in requirements, not QA. If there’s a material change – like switching banking providers or moving automated subscription billing – the team should run a new privacy assessment before that change goes live. For distributed teams, this also means keeping an eye on VPN access, credentials, and logs.
Ownership and Audit Evidence in Product Teams
Privacy by design doesn’t sit with one person or one team. Product owns the requirement, IT owns the systems, Legal owns compliance review, and Finance approves cost.
For audits, the most useful evidence usually includes:
- Data flow maps
- System access reports
- Documented policy updates
- Data logs and VPN records
That same line of thinking carries into launch, where defaults decide how much data gets collected by default.
Privacy by Default: Safer Settings at Launch and in Daily Use
Privacy by default starts before launch. The idea is simple: the safest settings should already be on before any user data is collected. That means collecting, sharing, storing, and showing the smallest amount of personal data unless there’s a clear reason not to.
In day-to-day work, this comes down to setting consent, tracking, access, and retention rules ahead of time. Start with the web interface and the admin panel. Privacy by default means setting up cookie consent boxes and ad blocker scripts the right way, along with admin-panel fields and permissions that shape how data is collected and shown to users. It also means access is restricted by default, so sensitive information is only available to the people who need it.
Who sets these defaults? Usually, a few teams share that job. RevOps and CRM owners affect these settings by choosing and configuring the systems that handle customer data. Marketing leads set consent and tracking rules. System admins control permissions. And one point often gets missed: these defaults need to be documented, not just turned on.
Ownership and Audit Evidence in Marketing and CRM Operations
For audits, it’s not enough to say the settings exist. Teams should be able to show the live default settings inside their tools. That can include:
- Cookie consent logs
- Admin-panel field configurations
- Documentation of secure sign-in protocols for sensitive data access
A default-settings policy and standard rules can also act as evidence that teams reviewed and applied those configurations in a consistent way. In marketing and CRM operations, the goal is to prove the default consent, retention, and access settings across the full stack.
Privacy by Design vs. Privacy by Default: Key Differences
The difference is practical: privacy by design shapes the system, while privacy by default shapes the launch settings.
A simple way to tell them apart is to look at scope, timing, ownership, and evidence.
Scope, Timing, Controls, Ownership, and Evidence Compared
| Feature | Privacy by Design | Privacy by Default |
|---|---|---|
| Scope | Product systems, data logic, and core processes | User settings, marketing forms, and day-to-day use |
| Timing | Pre-launch; during design and development | At deployment and during day-to-day use |
| Controls | Technical and design controls (e.g., deletion logic, encryption) | Configuration and user-setting controls (e.g., opt-in only) |
| Ownership | Product and Engineering teams | Marketing, CRM, and Operations teams |
| Audit Evidence | Architecture diagrams, code reviews, design documents | System logs, consent records, configuration snapshots |
Put plainly, Product and Engineering teams own the controls built into the product itself. Marketing, CRM, and Operations teams own the default settings people see and use day to day.
SME Examples from Product and Marketing Teams
The examples below show how this split plays out in product and marketing work.
On the product side, a team building a customer portal applies privacy by design by coding automated data deletion logic that runs after account closure and by setting role-based access so only certain employees can view PII. Those controls live inside the product. They aren’t bolted on later.
On the marketing side, a team setting up a newsletter sign-up form in a CRM applies privacy by default by asking for only an email address, making demographic or profiling fields optional, and keeping tracking cookies off until the user clearly opts in. By default, the form collects only email, and tracking stays off unless the user turns it on.
Conclusion: How SMEs Should Apply Both Principles Together
The comparison matters only if teams use both principles in the same workflow. Privacy by design shapes the system itself. Privacy by default shapes the settings users get on day one. SMEs need both. One deals with gaps during planning and building. The other deals with gaps at launch. So the issue isn’t choosing one over the other. It’s making both part of day-to-day work.
Without privacy by design, a product can collect too much data or leave it exposed. Without privacy by default, users can land in settings that are far too open from the start. Privacy can’t sit off to the side as a compliance box to check later. It needs to live inside the operating workflow. When Product, Marketing, and Operations all share the same view of what PII is being collected and why, teams can avoid duplicate data silos and make audit records easier to manage.
Key Points for Leaders
For leaders, that comes down to a few clear actions:
- Assign ownership early. Product and Engineering should own the controls built into the system. Marketing and Operations should own the default settings users see.
- Audit data collection before launch. Check every collection point and gather only the data you actually need.
- Set conservative defaults. Start with the most restrictive settings and use opt-in by default.
- Document decisions, settings, and access logs as standard deliverables.
- Use one shared privacy workflow across legal, IT, Product, Marketing, and Operations.
Tie each decision back to the same five dimensions: build-time controls, day-one defaults, clear ownership, and visible evidence.
FAQs
How do I know if a control is design or default?
A privacy by default control is turned on from the start. The user shouldn’t have to do anything. Its job is simple: limit data access or data collection unless someone clearly chooses otherwise.
Check the system’s starting setup to see whether it creates the lowest privacy impact by default. That can mean:
- least-privilege access
- consent gates before data is collected or shared
- data sharing turned off unless someone explicitly enables it
This shouldn’t live only in policy docs. You should be able to prove it with audit evidence, such as configuration baselines and internal security or compliance audit results.
What should an SME fix first to meet Article 25?
Start with a thorough audit of your data landscape. Look at five areas:
- Data readiness
- Process maturity
- Cultural readiness
- Technical infrastructure
- Financial capacity
This gives you a clear picture of where things stand before you make changes. Otherwise, it’s easy to pour time and money into systems that aren’t ready to support the work.
Next, map the data you collect and the reason you collect it. That simple step can reveal a lot. You may find duplicate records, missing fields, or data that no one actually uses.
From there, clean data at the source instead of fixing problems later. And make sure key data, like CRM records and financial records, lives in one central place so teams are working from the same information.
How often should privacy settings and data flows be reviewed?
Review privacy settings and data flows on a regular schedule, with timing based on operational risk and audit prep. A practical starting point is quarterly.
Take another look at how data moves across systems, confirm that user access permissions still make sense, and update controls so mistakes or drift show up early. Think of these reviews as part of ongoing security monitoring, not a one-and-done task.